
Today: administrative trust
Trust in operators
- Identitymanaged by third parties
- Serversrun by providers
- Permissionsset by administrators
- Contentdependent on operators
You have to trust the system.
VOOM Secure Collaboration
Data sovereignty instead of server dependency: server-blind communication for the highest security requirements – for government, defence, critical-infrastructure operators and regulated companies. Works on its own or as a sovereign complement to Microsoft 365.
SWISS BUILT / SWISS OWNED
Why now
Encryption protects data. But organisations still have to trust operators, administrators, identity systems and permission databases.
Sovereignty
Control over sensitive data and infrastructure is becoming a strategic issue.
Regulation
Switzerland’s Information Security Act, the FADP and FINMA rules, plus NIS2 and DORA in the EU, increase management accountability.
Crypto lifecycle
Crypto-agility is needed before the move to post-quantum algorithms becomes urgent.
Today: administrative trust
You have to trust the system.
With VOOM: cryptographic trust
Sovereign, verifiable and controlled by the organisation.
How VOOM works
The difference
| Criterion | Suites | Business messengers |  |
|---|---|---|---|
| Central administration | Yes | Yes | Yes |
| Server has no access to plaintext | Not by default | Yes | Yes |
| Organisation signs members and devices with its own key | No | User-based | Yes |
A question for your evaluation
Who signs which people and devices may enter your rooms? And can the operator add anyone without your signature?
Simplified positioning of typical product categories based on public vendor documentation, as of October 2026.
Six reasons for VOOM
Plaintext and keys exist only on authorised devices. There is no central store of readable data.
Neither servers nor operators, not even ENSIGNUM, can add anyone to a room without the organisation’s signature.
Policies, roles and revocation are enforced cryptographically. Revoking access means rotating keys.
Access only from a registered device; lost devices are locked out and keys rotated.
Operated on premises, with a Swiss partner or with a carrier. Control of the keys stays with the customer.
Algorithms are versioned and interchangeable. Post-quantum algorithms can be introduced without re-architecting the platform.
Features
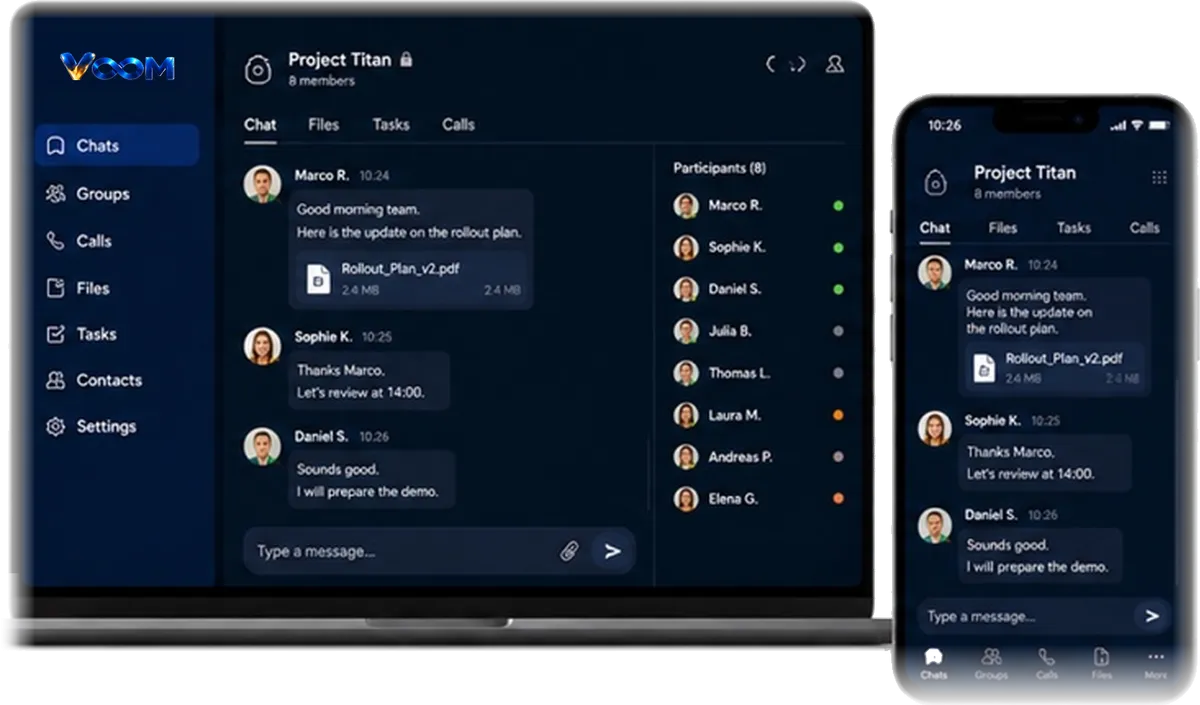
Cryptography: AES-GCM, ECDH P-256, HKDF with SHA-256, Ed25519, versioned and interchangeable.
On its own or with Microsoft 365: VOOM protects the most confidential communication.
Scope depends on the release; some features are in development. Details on request; for extensions, see Platform.
Trust Layer: platform and roadmap
Today VOOM protects the room. Next, the room becomes a protected case: messages, documents, tasks, approvals, evidence and AI jobs in one context, under one policy and end-to-end encrypted.
Forms, roles, approvals and AI jobs are declared, versioned and signed. AI drafts, a person releases.
A visible recipient with its own identity and a limited mandate. Proposals stay proposals until a person approves.
Contract review with external counsel, M&A data rooms and incident rooms, with or without Teams and AI.
Today
Chat, email, files and approvals run separately, and context gets lost.
With VOOM
One protected case for messages, documents, approvals and AI jobs.
Stages
2026–2028
Secure communication, signed members and devices, Safe Room
Beta today, Release 1.0 2027
from 2027
Clinical communication, tumour boards, telemedicine
Pilots planned
2027–2028
Cases, four-eyes approvals, case apps
planned
2028–2029
Knowledge and process assistance, controlled AI actions
planned
from 2029
Sovereign data exchange, audit trail on DLT, templates and SDK
planned
Stages 2 to 5 are planned and released only after product, security and customer reviews. Planned functions are not available; scope depends on the release, details on request.
Use cases
Protected teams, crisis and situation rooms
Protected mobile communication with central device control
Crisis and command communication, including during reportable incidents
Clinical communication, tumour boards, referral networks
Confidential deal and client communication
Secure communication as a service for business customers
One communication layer for the whole organisation
Sovereign operation, end-to-end encryption, membership signed by the organisation. On its own or as a complement to Microsoft 365.
Security
Our commitments before any production use:
Documented in writing.
By independent external testers.
Independent review of cryptography and protocols.
Every version signed, with a software bill of materials (SBOM).
No production release with open critical findings.
We are happy to walk you through the security architecture in person, under NDA if required. Arrange a meeting
Contact
Book a demo. We will show you how VOOM would work in your organisation.
Your contact
Dr. Stefan GrimmCo-founder and interim CEO, ENSIGNUM AG, Bernwww.voom.ch / www.ensignum.ch